Mathematical SemVer
API Contract Gatekeeper
Stop trusting human and AI commit messages blindly. Specter detects Trojan Breaking Changes across Rust and TypeScript public APIs in sub-5ms raw AST without invoking rustc or tsc.
# Plug & Play in < 5ms — No rustc / tsc setup required
- name: Audit API Contract & SemVer Gate
  uses: glastor-core/specter@v1
  with:
base-ref: ${{ github.base_ref || 'origin/main' }}Specter vs Compiler-Dependent Differ Tools
Traditional tooling forces CI runners to download GBs of compiler toolchains and compile hundreds of transitive dependencies just to inspect function signatures. Specter inspects raw AST in under 5 milliseconds.
| Capability / Metric | shield GLASTOR® Specter | cargo-semver-checks | @microsoft/api-extractor | Conventional Commits Alone |
|---|---|---|---|---|
| speed Execution Latency | < 5 ms (Zero-Compiler) | 2 – 8 minutes (rustdoc) | 30s – 2 minutes (tsc) | 0 ms (Manual text) |
| build_circle Compiler Dependency | Zero (No rustc / tsc) | Requires rustdoc JSON | Requires full tsc build | None |
| warning Trojan Breaking-Change Guard | Automated Mathematical Check | No commit intent check | No commit intent check | Blind human trust |
| layers Polyglot Monorepo Support | Rust (.rs) + TS / Deno (.ts) | Rust only | TypeScript only | N/A |
| memory Zero-Disk Git Extraction | In-memory (git show stream) | Full disk build required | Full disk build required | N/A |
| comment PR Sticky Comment & Diff | Automated Markdown + Diff | CLI output only | Markdown report file | None |
| verified_user Security & SBOM Compliance | SARIF 2.1.0 + CycloneDX 1.5 | Custom JSON only | Custom doc model only | None |
| savings FinOps CI Runner Minute Cost | ~$0.00 (<5ms runtime) | High CI minute cost | Moderate CI minute cost | $0 (Manual) |
Catch Trojan Breaking Changes in Real-Time
See how Specter's AST engine catches breaking changes hiding behind harmless fix: or chore: commit titles before they reach production.
PATCH (fix), but AST requires MAJOR (v1.0.0). PR gate failed to protect downstream consumers.
Retain original signature and introduce a new overload or verify_session_with_opts(...) to maintain backward compatibility.
Deterministic AST Contract Rules
Every rule in Specter maps directly to SemVer specifications. No fuzzy heuristics—just pure, reproducible AST semantics.
Function Signature Mutation
Public function parameter count, ordering, or types modified without backward-compatible default arguments.
Symbol Visibility Reduction
Public symbol deleted or demoted from pub / export to private or internal scope.
Optional Property to Required
TypeScript interface property mutated from optional (?) to required, breaking existing object instances.
Enum Variant Mutation
Public enum variant removed or payload tuple/struct altered, breaking pattern matching in client code.
Additive Public Surface
New public function, struct, or interface added in a fully backward-compatible manner. Requires MINOR bump.
Internal Logic / Docs Fix
Function body implementation, doc comments, or private helpers updated without touching public exported signatures.
Continuous Zero-Trust Verification Pipeline
Specter operates as the Stage 3 Gatekeeper in the complete GLASTOR® Core DevSecOps architecture, bridging pre-build AST test sharding and post-build SIMD binary inspection.
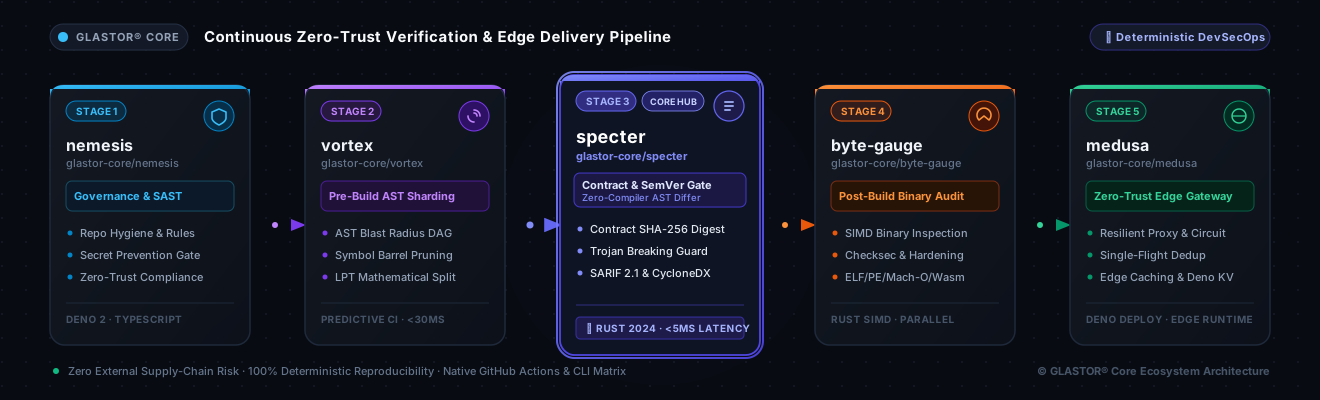
SAST Governance, secret leaks, and security compliance policies.
Pre-build AST dependency trees and hyper-fast test sharding.
Public API contract differ, Trojan breaking-change detection & SemVer gate.
Post-build SIMD binary inspection, section bloat, and compiler audits.
Zero-Trust edge gateway, MTLS, and runtime micro-perimeter defense.
Integrate into Any Workflow
Whether you run GitHub Actions, Kubernetes CI runners, or local dev machines, Specter installs in milliseconds with zero dependencies.
# In your Pull Request workflow (.github/workflows/ci.yml)
- name: Audit API Contract & SemVer Gate
  uses: glastor-core/specter@v1
  with:
base-ref: ${{ github.base_ref || 'origin/main' }}Everything You Need to Know
Answers to architectural, performance, and security questions from enterprise engineering teams.
How does Specter diff APIs in < 5 ms without invoking compilers? expand_more
What is a "Trojan Breaking Change"? expand_more
fix(gateway): improve error handling. Automated release pipelines blindly bump PATCH, inadvertently breaking hundreds of downstream consumers. Specter cross-checks commit intent with AST reality and halts the PR gate.
Does Specter support polyglot monorepos? expand_more
How does Specter integrate with GitHub Code Scanning & SBOM? expand_more
Why choose Specter over cargo-semver-checks? expand_more
cargo-semver-checks requires generating full rustdoc JSON for both the base commit and head commit, which takes 2 to 8 minutes on busy CI runners and consumes significant cloud minutes. Specter finishes in under 5 milliseconds, supports both Rust and TypeScript, and requires zero compiler installations.
Hardened for Zero-Trust Enterprise CI/CD
Engineered with strict zero-telemetry, offline-first execution, and cryptographically verified SLSA Level 3 build provenance.
100% On-Prem & Air-Gapped
Specter makes zero external network calls. Source code and AST representations never leave your runner boundary or air-gapped environment.
SLSA Level 3 & OpenSSF
Every release binary and Docker image is signed with GitHub OIDC SLSA provenance and passes OpenSSF Scorecard least-privilege standards.
Dual-Hub Governance
Governed under GLASTOR® Core corporate infrastructure with R&D hubs in Malaga TechPark (Spain/EU) and Argentina (LATAM).